

As enterprise infrastructures migrate massively to the cloud-native model, traditional authentication methods are showing their limitations. Passwords, even long and complex ones, remain the weakest link in the security chain, vulnerable to phishing, brute-force attacks, and credential theft.
Faced with these threats, FIDO2 technology is emerging as the ultimate solution to secure employee access while simplifying their daily lives thanks to "Passwordless".
What is FIDO2 technology?
FIDO2 is an open and global authentication standard, developed by the FIDO Alliance and the W3C. Unlike traditional systems, FIDO2 is based on the principle of public-key cryptography.
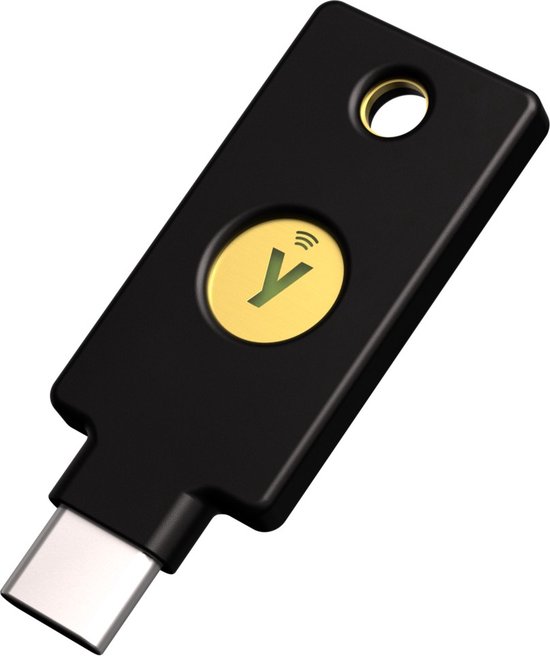
When an employee logs in, their physical security key (such as a YubiKey) generates a cryptographic key pair. The private key remains securely protected within the key's hardware component, while the public key is shared with the service (such as Microsoft Entra ID). No shared secrets (such as passwords) are transmitted over the network, making data interception completely ineffective for a hacker.
Passwordless: Remove the password to eliminate the risk
The first major advantage of FIDO2 keys in business is the adoption of a 100% Passwordless strategy.
Total immunity against phishing:
This is the main advantage. A fraudulent email can trick a human into entering their password or accepting an MFA (multi-factor authentication) notification. In contrast, a FIDO2 key is cryptographically linked to the exact URL of the legitimate website. If the user is on a phishing site that perfectly mimics the company's interface, the key will simply refuse to authenticate.
Simplifying the user experience:
No more passwords to remember, change every three months, or reset after vacation. The employee inserts their key, touches it (or confirms their fingerprint/PIN), and is logged in in less than two seconds.
Reduced IT support:
Requests to reset forgotten passwords often represent a significant portion of IT department support tickets. Passwordless technology eliminates this recurring operational cost.
The Perfect Fit with the Cloud-Native Ecosystem
Cloud-native architectures rely on flexibility, containerization, and always-on access to resources from anywhere. The traditional network perimeter of the enterprise has disappeared: the new perimeter is identity.
Native integration with modern IDPs:
FIDO2 keys integrate seamlessly and natively with cloud-based Identity and Access Management (IAM) solutions, such as Microsoft Entra ID (Azure AD), Okta, or Google Workspace.
Alignment with the Zero Trust philosophy:
The Zero Trust model dictates "never trust, always verify." FIDO2 keys provide the highest level of authentication assurance on the market. They indisputably guarantee that the person attempting to access a cloud-native application physically possesses the security token.
Securing privileged environments (DevOps/Admin):
In a cloud-native environment, compromised administrator access to a cloud console or Kubernetes cluster can be fatal. The mandatory use of FIDO2 keys for technical profiles (developers, system administrators) within an organization creates an impenetrable barrier against intrusions by malicious actors.
An essential strategic investment
Adopting FIDO2 security keys is more than just adding a technological gadget to your employees' toolkit. It's a strategic choice that propels your company's security into the modern era of cloud-native and zero-trust.
By definitively eliminating passwords and the flaws of traditional MFA, the FIDO2 standard offers the perfect compromise: bank-level security, impervious to phishing, combined with a disconcertingly smooth user experience.
If you need more information or simply an effective and reliable partner, feel free to make an appointment.